
A local-first personal finance app
Removed unsupported install methods (#108)
Rich Howelle6b9680a397b
diff --git a/docs/Installing/DockerWithNginx.md b/docs/Installing/DockerWithNginx.mddeleted file mode 100644index 097499f665..0000000000--- a/docs/Installing/DockerWithNginx.md+++ /dev/null@@ -1,452 +0,0 @@-----title: Docker with NGINX------## Hosting Actual on a home server with Docker and NGINX--Self-hosting ActualServer provides peace of mind and easy access to maintain your budgets. The process outline below creates an ActualServer with HTTPS (secure) access on port 9443. This is accomplished through Docker Compose and NGINX configured as a Reverse Proxy.---## Prerequisites-* Ubuntu Desktop or Server (v22.04 has been tested)-* Install OpenSSL-* Install Docker-* IP address or URL of your machine--### Ubuntu Desktop or Server--Machine running Ubuntu [Desktop](https://ubuntu.com/download/desktop) or [Server](https://ubuntu.com/download/server). This could be your personal desktop, a laptop, Virtual Machine (VM), server, etc...--### Install OpenSSL--```-sudo apt install openssl-```--### Install Docker--Follow the steps on Docker's Official page to [Install Docker Engine on Ubuntu](https://docs.docker.com/engine/install/ubuntu/).--### IP Address or URL of your machine--Your machine's IP address or URL is used to generate the self-signed certificates. Your browser uses these certificates to validate you've connected to the correct server.--If you run an internal DNS server and access your machine through a URL (like `ssh [email protected]`), you may want to use the URL to your machine. If not, or you're unsure, start with you machine's IP address.--The command below will show IP addresses for all network interfaces for your machine. Pick the one associated with the network you will use to access ActualServer.--```bash-ip addr show-```--**Note:** Typically you'll want to pick the address that looks like `192.168.1.123`. Don't worry if you pick the wrong IP address. The steps below show how to re-generate the certificates if you need to change the IP address.--## Setup Folders and Files--In this next section, a specific set of folders and files are created. These tell Docker Compose how to connect ActualServer to NGINX, setup NGINX to be a Reverse Proxy, and provide OpenSSL configuration for self-signed certificates.--### Create Folders--Choose a folder on your machine to create the following folders. This could be your home directory (good starting point) or another path on your hard drive.--```bash-cd <your folder choice>-mkdir -p actual-server/.certs-mkdir -p actual-server/reverse-proxy-mkdir -p actual-server/data-```--Here's how these folders will be used:-* `.certs` will store the self-signed private key and public certificate for the NGINX Reverse Proxy.-* `reverse-proxy` will contain the `Dockerfile` and `nginx.conf` files used to pull the latest NGINX image and customize NGINX to run as a Reverse Proxy.-* `data` contains the server-side storage location for your synced Actual Budgets. This folder can be manually backed up. It persists outside of the Docker container (i.e. it won't be deleted when you stop or remove the container).--### Create Files--Let's create the four files needed to configure Docker Compose, NGINX, and prepare for self-sign certificate generation.--* `openssl.conf` assists with OpenSSL self-signed certificate generation-* `Dockerfile` and `nginx.conf` configure NGINX to run as a Reverse Proxy-* `docker-compose.yaml` instructs Docker Compose to spin up two images, ActualServer and NGINX, they are connected via a Docker Network---#### `openssl.conf`--Create `openssl.conf`-```bash-cd actual-server/.certs-nano openssl.conf-```--Past the following contents into `openssl.conf` and replace `123.123.123.123` with your machine's IP address or URL. Be sure to update ***both*** lines below.-```-[req]-default_bits = 2048-distinguished_name = req_distinguished_name-req_extensions = req_ext-x509_extensions = v3_ca--[req_distinguished_name]-countryName = Country Name (2 letter code)-countryName_default = US-stateOrProvinceName = State or Province Name (full name)-stateOrProvinceName_default = New York-localityName = Locality Name (eg, city)-localityName_default = New York-organizationName = Organization Name (eg, company)-organizationName_default = Self Signed Certificate-organizationalUnitName = organizationalunit-organizationalUnitName_default = ActualServer-commonName = Common Name (e.g. server FQDN or YOUR name)-commonName_default = 123.123.123.123--[req_ext]-subjectAltName = @alt_names--[v3_ca]-subjectAltName = @alt_names--[alt_names]-DNS.1 = 123.123.123.123-```--A quick note on the file above:-* The most important lines above are `commonName_default` and `DNS.1`. These specify the name of the machine running ActualServer. When your browser trusts these certificates AND the name of the machine matches the certificates, your browser will show the "secure" or "green" icon for HTTPS.---#### `Dockerfile`--Create `Dockerfile`-```bash-cd actual-server/reverse-proxy-nano Dockerfile-```--Past the following contents into `Dockerfile`-```-FROM nginx:latest--RUN rm /etc/nginx/conf.d/default.conf-COPY nginx.conf /etc/nginx/conf.d/nginx.conf-```--Here's what this file is doing:-* `FROM nginx:latest` instructs Docker to pull the latest NGINX image when we call `build` further down in the process.-* `RUN rm /etc/nginx/conf.d/default.conf` removes the default NIGNX config. This prevents the "Welcome to nginx!" default screen from showing which can interfere with HTTP -> HTTPS redirection.-* `COPY nginx.conf /etc/nginx/conf.d/nginx.conf` loads the Reverse Proxy configuration file into the image.---#### `nginx.conf`--Create `nginx.conf`-```bash-cd actual-server/reverse-proxy-nano nginx.conf-```--Past the following contents into `nginx.conf` and update ***both*** paths below with `<your folder choice>`.-```-#ssl on; # deprecated, use ssl parameter on the listen directive-ssl_session_cache builtin:1000 shared:SSL:10m;-ssl_protocols TLSv1 TLSv1.1 TLSv1.2;-ssl_ciphers HIGH:!aNULL:!eNULL:!EXPORT:!CAMELLIA:!DES:!MD5:!PSK:!RC4;-ssl_prefer_server_ciphers on;--proxy_read_timeout 90;--# # Redirect from HTTP to HTTPS-# server {-# listen 80; # Listen for all traffic on port 80-# server_name _; # Matches any hostname-# return 301 https://$host:9443$request_uri; # 301 tells browser this is a permanent redirect and specifies the HTTPS version of the original request on port 80-# }--server {- listen 9443 ssl;- # server_name actualserver.internal.mydomain.com;-- ssl_certificate /<your folder choice>/actual-server/.certs/selfhost.crt;- ssl_certificate_key /<your folder choice>/actual-server/.certs/selfhost.key;-- location / {- proxy_pass http://actualserver:5006/;-- proxy_set_header X-Real-IP $remote_addr;- proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;- proxy_set_header X-Forwarded-Proto $scheme;- }-}-```--A couple notes on the file above:-* This Reverse Proxy is setup to serve ActualServer on port 9443. Feel free to change this port. *Make sure* to also update the `ports` section of the `nginx` in `docker-compose.yaml` below.-* It is possible to run multiple Reverse Proxies with the same NGINX instance. The commented line `# server_name actualserver.internal.mydomain.com` is intended to provide a starting point if you'd like to pursue this. Recommend looking up examples on how to use `server_name` with NGINX.-* The `Redirect from HTTP to HTTPS` section is provided as a starting point if you'd like to enable NGINX to automatically redirect browsers to SSL on port 9443. If you enable this section, also un-comment line `80:80` in `docker-compose.yaml` below.---#### `docker-compose.yaml`--Create `docker-compose.yaml`-```bash-cd actual-server/-nano docker-compose.yaml.conf-```--Past the following contents into `docker-compose.yaml` and update ***both*** paths below with `<your folder choice>`.-```-version: '2.1'-services:- actual-server:- image: jlongster/actual-server:latest- restart: always- # ports:- # - 5006:5006- volumes:- - /<your folder choice>/actual-server/data:/data- networks:- frontend:- aliases:- - actualserver-- nginx:- build: ./reverse-proxy- restart: always- ports:- # - 80:80- - 9443:9443- volumes:- - /<your folder choice>/actual-server/.certs:/etc/nginx/certs:ro- networks:- frontend:--networks:- frontend:-```--A couple notes on the container and network setup:-* Two images are spun-up. One is the NGINX Reverse Proxy which uses the `reverse-proxy/Dockerfile` to build the image. The other is ActualServer.-* NGINX and ActualServer are networked together by the `frontend` network which is not publicly accessible.-* Port `5006` for ActualServer is commented out. This provides HTTP (non-encrypted) access. Recommend enabling this only for debugging issues.-* ActualServer is given the alias `actualserver` on the `frontend` network. This sets the DNS name for ActualServer on the `frontend` network. Why do this? It enables NGINX's configuration to be more human-readable. See this line: `proxy_pass http://actualserver:5006/`-* Port `9443` is made public for the NGINX image. This enables you to hit the Reverse Proxy which forwards your requests to ActualServer.---## Certificates--In this section, we'll create self-signed certificate for NGINX to use to encrypt the traffic between your browser and NGINX.--### Generate Certs--Run the following command to generate certs, press `ENTER` at each prompt without changing the content.--```bash-cd actual-server/.certs-openssl req -x509 -nodes -days 365 -newkey rsa:2048 -keyout selfhost.key -out selfhost.crt -config openssl.conf-```--### Re-generate Certs--To re-generate the certificates (change your machines IP address or URL), delete the key and certificate, and then generate certs.--```bash-cd actual-server/.certs-rm selfhost.*-openssl req -x509 -nodes -days 365 -newkey rsa:2048 -keyout selfhost.key -out selfhost.crt -config openssl.conf-```---## Managing The Server--This section covers typical actions required to manage the server--### Start Server--```bash-cd actual-server/-sudo docker compose up -d-```--**Note:** Omit `-d` to leave the console connected to the containers. This enables status and error messages to show. When done viewing the status and error messages, press `CTRL+C` to stop the containers, then start the server with `-d`.--### Stop Server--```bash-cd actual-server/-sudo docker compose down-```--**Note:** Your budgets are saved outside the Docker containers in folder `actual-server/data` on your machine. They will not be deleted when you bring the server down.--### Configuration File Change--When `Dockerfile` or `nginx.conf` files are modified, run `build` to create new NGINX image with the changes, then run `up` to re-launch the server.--```bash-cd actual-server/-sudo docker compose build-sudo docker compose up -d-```--When the certificates or `docker-compose.yaml` files are modified, stop and then start the server.-```bash-cd actual-server/-sudo docker compose down-sudo docker compose up -d-```--### Backing up the Server--This section outlines one method of performing a server backup.--First, choose a location to store the backups: create a parent folder, create a snapshot folder-```bash-mkdir /<backup folder>/actual-server-backups-cd /<backup folder>/actual-server-backups-mkdir 20230101 # This is the snapshot folder-```--Then, stop the server-```bash-cd actual-server/-sudo docker compose down-```--Copy the contents of `data` into the snapshot folder-```bash-cd actual-server/-cp -R data/ /<backup folder>/actual-server-backups/20230101-```--Last, start the server-```bash-cd actual-server/-sudo docker compose up -d-```--### Restoring the Server--This section outlines one method of restoring a server backup.--First, stop the server-```bash-cd actual-server/-sudo docker compose down-```--Delete the server's `data` folder-```bash-cd actual-server/-rm -rf data-```--Copy the desired backup-```bash-cd actual-server/-cp -R /<backup folder>/actual-server-backups/20230101/data/ .-```--Last, start the server-```bash-cd actual-server/-sudo docker compose up -d-```--When you browse to your ActualServer, the budgets should reflect the restored backup.---### Docker Image Updates--When new versions of ActualServer or NGINX are released, perform the following commands to pull the new images and re-launch the server.--**Note:** Recommend performing a backup BEFORE upgrading ActualServer images!--```bash-cd actual-server/-sudo docker compose pull-sudo docker compose up -d-```--## Browse to ActualServer--Your ActualServer is now usable by any device on your local network.--Access your server with the URL below (replace `123.123.123.123` with the IP address or URL you configured):-```-https://123.123.123.123:9443-```--## Debugging Issues--Here are a couple issues and solutions when setting up ActualServer with NGINX Reverse Proxy--### I've started the server, what do I look for?--Launch the server with `sudo docker compose up` (omit `-d` so the logs are shown). Look for any errors.--The following are "good" outputs:-```-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker processes-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 20-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 21-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 22-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 23-actual-server-actual-server-1 | Listening on 0.0.0.0:5006...-```--As browsers access ActualServer, NGINX will log the requests to the console.--Outputs to the console like `exited with code 1` and others may indicate something is wrong with the configuration or files.--### Troubleshooting network access--Recommend launching the server with `sudo docker compose up` (omit `-d`).--Use the `curl` command to see if NGINX is reachable (use HTTP, it will cause NGINX to return the error in plain-text):-```-curl http://123.123.123.123:9443-```--You should get a response similar to this:-```-<html>-<head><title>400 The plain HTTP request was sent to HTTPS port</title></head>-<body>-<center><h1>400 Bad Request</h1></center>-<center>The plain HTTP request was sent to HTTPS port</center>-<hr><center>nginx/1.23.3</center>-</body>-</html>-```--Also check the console running the server. You should see an access attempt recorded by NGINX (look at the last line).-```-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 22-actual-server-nginx-1 | 2023/01/14 15:34:11 [notice] 1#1: start worker process 23-actual-server-actual-server-1 | Listening on 0.0.0.0:5006...-actual-server-nginx-1 | 123.123.123.123 - - [14/Jan/2023:15:34:33 +0000] "GET / HTTP/1.1" 400 255 "-" "curl/7.81.0" "-"-```--If you've made it to this point, the server is running and properly configured.--A couple thoughts:-* The IP address chosen in section **IP Address or URL of your machine** may not be accessible by other devices on your network. Recommend using `ping` between machines to verify the correct IP address and then update the server configuration.-* There may be an issue with your machine's firewall (unlikely, Docker controls the firewall).-* There may be an issue with your home network setup.---### NGINX continuously shows `exited with code 1`--If you start ActualServer and see NGINX scrolling the error below-```-actual-server-nginx-1 exited with code 1-actual-server-nginx-1 exited with code 1-actual-server-nginx-1 exited with code 1-````--you may have a configuration file issue. Recommend double checking the paths to the certificates. Verify they're correct in **both** `docker-compose.yaml` and `nginx.conf`---## References--* https://www.humankode.com/ssl/create-a-selfsigned-certificate-for-nginx-in-5-minutes/-* https://serverfault.com/questions/828130/how-to-run-nginx-ssl-on-non-standard-port#828135\ No newline at end of filediff --git a/docs/Installing/Terraform.md b/docs/Installing/Terraform.mddeleted file mode 100644index a9d4099763..0000000000--- a/docs/Installing/Terraform.md+++ /dev/null@@ -1,12 +0,0 @@-----title: 'Terraform'------## Installing Actual using Terraform--Terraform is a configuration as code tool that allows declarative deployments on various cloud-providers.--The community has provided Terraform configuration examples and guides for the following providers:--[Fly.io](https://actualbudget.github.io/docs/Installing/fly/Fly-terraform/)diff --git a/docs/Installing/Unraid.md b/docs/Installing/Unraid.mddeleted file mode 100644index 60335237a9..0000000000--- a/docs/Installing/Unraid.md+++ /dev/null@@ -1,103 +0,0 @@-----title: 'Unraid'------## Hosting Actual with [Unraid](https://unraid.net/)--## Initial setup-### Using Community Apps--1. If you don't have the CA plugin installed, install it now. Please read through all of the instructions before starting.-As always, backup your data by exporting from the web interface prior to making any configuration changes.-The current Actual Unraid CA was defined and maintained by hofq. Problems specifically with the-unraid template (not Actual itself) should be addressed to that repo, which can be found [here](https://github.com/hofq/docker-templates/issues/new/choose).-1. Search for "actualserver" in [Community Apps](https://unraid.net/community/apps?q=actualserver) and-select the one by Kippenhof (the only one at this time).-1. Click Install.-- 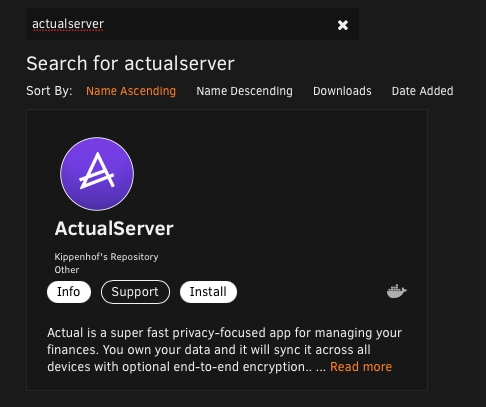---### Using Docker without Community Apps--1. Create a new image and follow the guidelines below to configure the parameters-This image is not very complex, and can easily be configured in the web interface.-Follow the instructions below to configure the Repository, Data volume, WebUI port, and HTTPS keys necessary for running the image.---## Setting up data persistence--To avoid losing data when updating your image, it is recommended to setup a persistent volume.-This step is also necessary for sharing the HTTPS key/cert combination into the image.--1. Towards the bottom the template, select `Add another Path, Variable, Label or Device`,-1. In the popup, fill in the following details - changing your host location to match your setup:- 1. Name the path `Data`,- 1. Set the Container Path: `/data`,- 1. Set the Host Path (eg) `/mnt/user/appdata/actual`-- 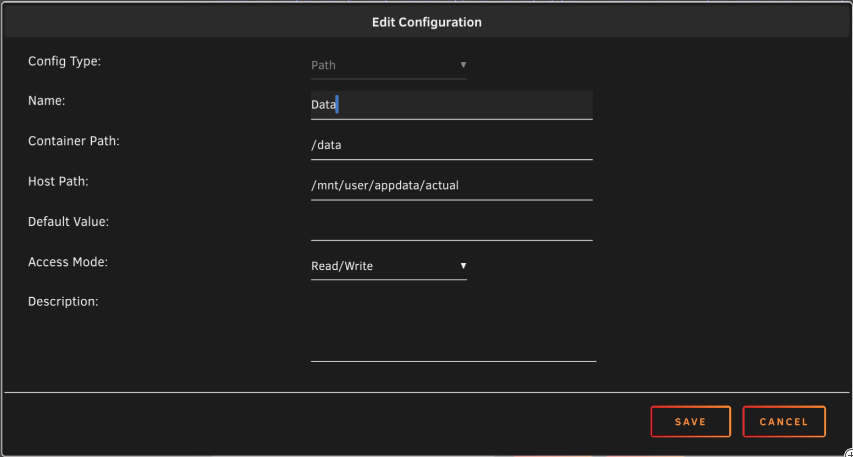-- This creates a directory named `actual` on your server and maps the container's `/data` folder to- that directory on your Unraid server. This persists the data to the server. You can then make- backups of the database from the host path you specified above.--1. Click "Apply", watch the container pull the image and start up. Login to Actual as outlined in-the other guides.--(Note: It's generally wise to have a manual backup strategy just in case. Two is one, one is none!)---## Changing the image source--If you'd like to point the Actual Community App to a different image, it's simple to do so.--1. First, backup your data. Safety first! See the documentation on exporting your data for specific-instructions.-1. On the settings page for the Actual CA, locate the `repository` field.- -1. Update this value to point to the dockerhub image of your choice. Eg, to use the official image- change this value to [`jlongster/actual-server`](https://hub.docker.com/r/jlongster/actual-server) or [`ghcr.io/actualbudget/actual-server:latest`](https://ghcr.io/actualbudget/actual-server)- -1. Confirm that the correct image is pulled. The `By:` section should read `By:-ghcr.io/actualbudget/actual-server:latest` (or whichever image source you have chosen to use).-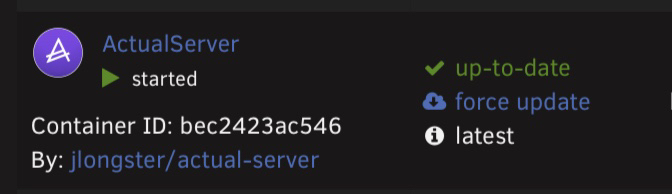--## Advanced-### Creating HTTPS Certificates--New versions of Actual depend on HTTPS to be enabled (see [Enabling SharedArrayBuffer Access](/Troubleshooting/SharedArrayBuffer)). To create your own certificate on Unraid, open up a terminal into your server to follow these steps:--1. Change directory into your shared data folder (see "Setting up data persistence" above)-1. Create a new folder, "keys"-1. Change directory into the "keys" folder-1. Generate a certificate and private key combo by running `openssl req -x509 -nodes -days 365 -newkey rsa:2048 -keyout actual.key -out actual.crt`-1. In the Docker settings on the WebUI, create a new Variable `ACTUAL_HTTPS_KEY` and set the value to the path of the newly created key, `/data/keys/actual.key` (note: this is the value of the path _inside_ the docker container)-1. Similarly to step 5, create a new Variable `ACTUAL_HTTPS_CERT` and set the value to `/data/keys/actual.crt`-1. The next time the Actual Docker container is started, access the WebUI and accept the self-signed certificate.---### Map WebUI Port to container--Assuming the default port of 5006, map TCP host port 5006 to Docker port 5006.---### Add WebUI URL--By default, Actual server runs on port 5006. To enable the WebUI button on the Docker page, go into the advanced Docker settings and set the WebUI to value `https://[IP]:[PORT:5006]/`---### If you already had an alternate image running:--1. BACKUP YOUR DATA. Safety first!-1. Stop your container and click `edit`.-1. Change the repository field to point to the dockerhub image of your choice. See the above section- if needed.-1. Click Apply, and watch the container do its magic and swap out the image.-1. Restart the container if it didn't restart automatically.-1. On the `Docker` tab, enable `Advanced View` and confirm that you are now running the image you- entered in step 3.- -1. Try logging in to your budget like normal. You may have to log in again or you may get a sync-error that says you need to revert to another version. Once you get through all that, you should be-good to go. If it went badly, hopefully you didn't skip step 1!diff --git a/docs/Installing/fly/Fly-terraform.md b/docs/Installing/fly/Fly-terraform.mddeleted file mode 100644index f834cf227f..0000000000--- a/docs/Installing/fly/Fly-terraform.md+++ /dev/null@@ -1,53 +0,0 @@-----title: 'Deploying Actual with terraform'------# Deploying Actual on fly.io with terraform--## Requirements--1. [Install terraform](https://learn.hashicorp.com/tutorials/terraform/install-cli).-1. Ensure you've [installed the flyctl utility](https://fly.io/docs/flyctl/installing/) and logged- in.-1. Copy the `terraform` subdirectory of `actual-server` [(link)][tf-dir].--## Terminal 1: Setup--1. Enter the `terraform` subdirectory of `actual-server`.-1. Log in to fly.io by running- ```sh- fly auth login- ```-1. Set your fly.io API key as an evironment variable- ```sh- export FLY_API_TOKEN=$(fly auth token)- ```--## Terminal 2: Open Wireguard Tunnel--1. In a separate terminal, run- ```sh- fly machines api-proxy- ```- -- This will open a wireguard tunnel from your local machine to fly's infrastructure allowing- terraform to access the `machines` api.--## Deploy--1. Return to terminal 1.-1. Initialize terraform by running the following command in the `terraform` directory:- ```sh- terraform init- ```-1. Update the `ex.tfvars` file (or use your preferred method of variable provision), then:- ```sh- terraform apply -var-file=ex.tfvars- ```-1. Review the plan, and enter `yes` if it matches expectations.-- --You should now have a running app! Open your [fly.io dashboard](https://fly.io/dashboard/) to-inspect any additional details.\ No newline at end of filediff --git a/docs/Installing/fly/Fly.io.md b/docs/Installing/fly/Fly.io.mdindex c5108bef4f..d913fbae66 100644--- a/docs/Installing/fly/Fly.io.md+++ b/docs/Installing/fly/Fly.io.md@@ -15,10 +15,9 @@ step unclear, [contact us](/Contact) for support.## Deployment methodsFly offers a variety of ways to get an application deployed on their infrastructure. We currently-have community contributed documentation for the following deplyment methods-- Deploying from a clone of the main git repository [(link)][git-guide]-- Deploying from a published container image [(link)][image-guide]-- Deploying an image with Terraform [(link)][terraform-guide]+have community contributed documentation for the following deployment methods+- Deploying [from a clone of the main git repository][git-guide]+- Deploying [from a published Docker container image][image-guide]Each of these methods come with tradeoffs.diff --git a/docs/Installing/overview.md b/docs/Installing/overview.mdindex bd2d67be22..2c876d26c6 100644--- a/docs/Installing/overview.md+++ b/docs/Installing/overview.md@@ -4,14 +4,13 @@ title: 'Installing Actual'Unlike most web apps, you’ll need to install Actual on a computer to get the full benefit out of it. While you could use Actual without running a server, we strongly recommend a server to ensure that your budget is saved and can be synced across multiple browsers and devices.-While running a server can be a complicated endeavor, we’ve tried to make it fairly easy to set up and hands-off to maintain. Choose one of the following options to get started:+While running a server can be a complicated endeavour, we’ve tried to make it fairly easy to set up and hands-off to maintain. Choose one of the following options to get started:- If you’re not comfortable with the command line and are willing to pay a small amount of money to have your version of Actual hosted on the cloud for you, we recommend [PikaPods](PikaPods.md).- If you’re willing to run a few commands in the terminal:- [Fly.io](fly/Fly.io.md) offers free cloud hosting. (Make sure you read the section about [persisting your data](fly/Fly-persisting.md)!)- You could [directly install Actual locally](Local/your-own-machine.md) on macOS, Windows, or Linux if you don’t want to use a tool like Docker. (This method is the best option if you want to contribute to Actual!)- - If you want to use Docker, we have instructions for [running Actual directly](Docker.md) inside Docker or [behind an nginx proxy that offers HTTPS support](DockerWithNginx.md).-- If you have a home server or a NAS running [Unraid](Unraid.md) or [Synology](synology/synology.md), we have instructions for installing Actual on those platforms.+ - If you want to use Docker, we have instructions for [using our provided Docker containers](Docker.md).Once you’ve set up your server, you can [configure it](Configuration.md) to change a few of the ways it works.diff --git a/docs/Installing/synology/synology-reverse-proxy.md b/docs/Installing/synology/synology-reverse-proxy.mddeleted file mode 100644index 2836b8946a..0000000000--- a/docs/Installing/synology/synology-reverse-proxy.md+++ /dev/null@@ -1,38 +0,0 @@-----title: 'Enabling a Reverse Proxy'------1. If you don't have a registered hostname, Synology offers a free service that provides one. You can also use your existing provider. This information is found in the **Control Panel** in the **External Access** menu.---2. Navigate to the **Login Portal** menu and click on the **Advanced** tab. Then click on the **Reverse Proxy** button.----:::note-You may come back to this step later.-:::--3. Add a new rule. Give the reverse proxy rule a name. Set the hostname to whatever you like. In this example, it is set to budget (hostname set in step 1). A reverse proxy uses the port `443` SSL port. Enable HSTS and set the destination to your Actual docker container. There is an option for access control restriction. This can be used to limit the IP addresses that are allow to access this reverse proxy. It is especially useful if you want to use a VPN connection in addition to a reverse proxy.----4. Your reverse proxy needs an SSL certificate. We can add one from the **Security** menu under the **Certificate** tab.----5. Choose a certificate from **Let's Encrypt** if you don't already have a certificate you want to use.----6. Type in your new domain name you generated from the Reverse Proxy setup in step 3.----Once all of these settings are applied, you may have to forward port `443` from your router to your Synology. A DNSMASQ rule may also have to be set to use the hostname on your local network. Check your routers documentation if you need instructions on setting up port forwarding rules and DNSMASQ.--If you have a VPN set up for your local network, it is possible to restrict usage of your new reverse proxy Actual container to only devices on your local network or VPN. Go back to the menu in step 3 and add an **Access Restriction** rule.--The first line should represent your local area network IP address range, while the second line should represent your VPN IP address range. Once this rule is set up, edit your reverse proxy rule and apply the Access Control profile.--diff --git a/docs/Installing/synology/synology-watchtower.md b/docs/Installing/synology/synology-watchtower.mddeleted file mode 100644index 053615c44f..0000000000--- a/docs/Installing/synology/synology-watchtower.md+++ /dev/null@@ -1,50 +0,0 @@-----title: 'Synology Automatic Updates'------:::note This page details a method of automatically updating actual that uses 3rd party software not maintained or written by the development team of Actual Budget. The continued maintenance, applicability or potential data loss is not guaranteed by Actual when using this software. Direct all bug requests with regards to automatically updating Docker containers to the maintainer of the package chosen.-:::-:::caution These instructions grant root access to a 3rd party package. This is an inherent security risk. If you are uncomfortable with this risk, this method may not be suitable for you.-:::--Updating containers on a Synology isn't hard, but it can be tedious if you have to do it too many times. This page will provide instructions for one method to automate the task.--1. Navigate to the **Docker** application----2. Search for and download **containrrr/watchtower** using the **latest** tag.----3. Navigate to the **Control Panel** and go to the **Task Scheduler** menu.----4. Create a new **Scheduled task/User defined script**.----5. Change the user to **root** on the **General tab**----6. Change the schedule to **Run on the following date** and **Do not repeat** on the **Schedule tab**----7. Add the following string to the **Task Settings** tab----```docker run -d --name watchtower -v /var/run/docker.sock:/var/run/docker.sock containrrr/watchtower --interval 86400 --cleanup```--* The -v command allows Watchtower to connect to Dockers socket and update running containers.-* The --interval command is in seconds. 86400 will set an update interval every 24 hours.-* The --cleanup command will delete old images after downloading and installing new ones to reduce clutter.--8. Press OK. Select the newly created scheduled task and select the **Run** command.----You can now go to the Docker application and you should have a newly created watchtower container that will automatically update your Actual container any time there is a new release. You can also delete the newly created schedule if you wish.diff --git a/docs/Installing/synology/synology.md b/docs/Installing/synology/synology.mddeleted file mode 100644index fa5e1926ab..0000000000--- a/docs/Installing/synology/synology.md+++ /dev/null@@ -1,97 +0,0 @@-----title: 'Synology'------[reverse-proxy]: ./synology-reverse-proxy-[watchtower]: ./synology-watchtower--# Synology DSM 7.1--Actual can be hosted on a Synology Diskstation where total control of your data can be maintained.--## Installing Docker--1. Navigate to Package Center.--2. Search for Docker and install the package.----## Create a folder for your budget data to reside--1. Navigate to **File Station**--2. A folder named **docker** should be along the left hand side. Open the docker folder and create a new folder inside named **actual**.--3. If you will be using multiple containers for actual for multiple users, you may name this something more descriptive for each user.----## Installing Actual--1. Open the Applications menu and open Docker.--2. Select the Registry menu item on the left hand side.--3. Search for jlongster/actual-server----4. Select the **Image** and then press the download button. Select the **latest** tag.----5. Once the image is downloaded, navigate the the **Image** menu item.--6. Select the newly downloaded image for actual-server, and press the **Launch** button at the top of the screen.----7. A new dialog menu will appear and ask for network settings. **Use the selected networks** (bridge) and press **Next**.----8. Give your new container a name, or use the default. **Enable auto-restart**. **Next**. The remaining options can stay at the default values.----9. **Add** ports to your container. DSM uses port 5006 for another application, so we will give Actual a different port. Set the **Local** port to 5007. Set the **Container** port to 5006. **Next**.----10. **Add Folder**, select the folder that was created above using **File Station**. Set the **Mount path** to **/data**. **Next**.------11. A summary of your container will be displayed. Press **Done**.----You now have Actual installed on your Synology NAS. Now let's try to access it.--Using your preferred web browser, try typing the IP address of the NAS into the address bar followed by port 5007. I.e. http://(ip address):5007-If you see the welcome page to Actual, that's great! If not, you may have your firewall enabled and need to allow the port.--## Letting Actual through the firewall--1. Navigate to the **Control Panel**.--2. Navigate to the **Security** icon.----3. Click on the **Firewall** tab and then select **Edit Rules**----4. Create a new rule that allows port 5007. This should be place before the final rule, which is usually a DENY rule for all remaining ports.------5. Select **OK** and try connecting to Actual again.--If you are only wanting to access Actual on your home network, this is the end of the instructions. If you want to automatically update Actual when there is a new release or access Actual when you are away from your home network, read on.diff --git a/sidebars.js b/sidebars.jsindex 8b213d00cf..694ae97d36 100644--- a/sidebars.js+++ b/sidebars.js@@ -80,8 +80,7 @@ const sidebars = {items: ['Installing/fly/Fly-prerequisites','Installing/fly/Fly-git',- 'Installing/fly/Fly-image',- 'Installing/fly/Fly-terraform',+ 'Installing/fly/Fly-image','Installing/fly/Fly-updating','Installing/fly/Fly-persisting',],