
🐸 Rybbit - open-source and privacy-friendly alternative to Google Analytics that is 10x more intuitive.
Enhance layout and metadata for improved SEO and user experience
Bill Yang1748a2a7404b
diff --git a/docs-v2/content/blog/data-privacy-2025.mdx b/docs-v2/content/blog/data-privacy-2025.mdxnew file mode 100644index 000000000..cda821ea3--- /dev/null+++ b/docs-v2/content/blog/data-privacy-2025.mdx@@ -0,0 +1,188 @@+---+title: 9 Data Privacy Best Practices for 2025 That Actually Work+date: 2025-08-20+tags: ['data privacy']+author: Bill Yang+---++Feeling lost in the shifting world of data privacy?Feeling lost in the shifting world of data privacy? You're not alone. With regulations like GDPR and CCPA getting stricter and third-party cookies finally crumbling, keeping user data safe while gathering meaningful insights is tougher than ever. The old playbook is obsolete, and generic advice just won't cut it anymore. What businesses need are practical, forward-thinking strategies that build trust and respect user autonomy.++This guide is designed to deliver just that. We're diving straight into nine essential **data privacy best practices** that go beyond the obvious "have a privacy policy" platitudes. We'll cover everything from the foundational principles of data minimization and Privacy by Design to the technical specifics of implementing cookieless tracking with modern tools like Rybbit Analytics. Forget vague theories; you'll get actionable steps to fortify your data handling, ensure compliance, and build a privacy-first culture that becomes a competitive advantage.++You'll leave with a clear roadmap for not just meeting legal requirements, but for creating a more transparent and trustworthy relationship with your users. Let's get started on a smarter, more secure approach to data that works for everyone.++## 1. Data Minimization++Data minimization is exactly what it sounds like: collecting only the absolute minimum amount of personal data required to achieve a specific, defined purpose. Think of it as the Marie Kondo method for data collection. If a piece of data doesn't spark joy (or, more accurately, isn't essential for a function), you don't collect it. This principle is a cornerstone of modern data privacy best practices and a key requirement in regulations like GDPR.++++The less data you hold, the lower your risk. A data breach becomes far less catastrophic if the compromised database contains non-sensitive, aggregated information instead of a treasure trove of personal details. Companies like Apple champion this by processing data on-device whenever possible, while the search engine DuckDuckGo simply doesn’t store user search history at all.++### How to Implement Data Minimization++Getting started is about asking one simple question for every data point you collect: **"Do we *really* need this?"**++* **Conduct Regular Data Audits:** Scrutinize your forms, databases, and analytics events. Are you still collecting data for a feature you retired last year? Identify and eliminate any data collection that no longer serves a clear, active purpose.+* **Automate Data Retention:** Don't hoard data forever. Implement automated policies that delete or anonymize user data after a set period, such as 90 days for inactive accounts. This prevents your data liability from growing indefinitely.+* **Embrace Privacy-by-Design:** Build minimization into your product from the ground up. Instead of asking for a user's full birthdate for an age gate, for example, just ask for a yes/no confirmation that they are over 18. This is a practical application of one of the most important data privacy best practices.++## 2. Encryption at Rest and in Transit++Encryption is the digital equivalent of locking your data in an uncrackable safe. It involves scrambling data so that it's unreadable to anyone without the specific key to unlock it. This crucial practice applies to data in two states: when it's being sent over a network ("in transit") and when it's stored on a server or hard drive ("at rest"). Without it, sensitive information is just plain text, open to interception.++++This dual-layered approach ensures comprehensive protection. Think of WhatsApp’s end-to-end encryption, which secures messages as they travel between phones, or the server-side encryption that cloud providers like AWS and Azure apply to your stored files. Even if a cybercriminal breaches a server, encryption at rest makes the stolen data completely useless. This makes robust encryption a non-negotiable component of modern data privacy best practices.++### How to Implement Encryption++Effective encryption starts with using proven standards and managing your keys like a hawk. **Weak encryption is almost as bad as no encryption at all.**++* **Use Strong, Standard Algorithms:** Don't reinvent the wheel. Implement industry-standard algorithms like AES-256 for data at rest and TLS for data in transit. These are battle-tested and trusted globally.+* **Automate Key Management:** Manually managing encryption keys is a recipe for disaster. Use a key management service (KMS) to automate key rotation, storage, and access control. This drastically reduces the risk of human error.+* **Encrypt Everything, Everywhere:** Audit all your data touchpoints, from web forms and mobile app APIs to databases and internal backups. Apply encryption consistently across the entire data lifecycle to ensure there are no weak links in your security chain.++## 3. Access Control and Authentication++Not everyone in your organization needs access to every piece of user data. Access control and authentication are the digital bouncers for your data, ensuring only authorized individuals get past the velvet rope based on their specific role and a verified need-to-know. This foundational security principle prevents both accidental exposure and malicious internal threats.++++This framework is about applying the principle of least privilege, where employees have access only to the data absolutely necessary to perform their jobs. For example, a marketing analyst might need aggregated website traffic data, but they almost certainly don't need access to individual user account details. Companies like Microsoft and Google build this into their enterprise suites with tools like Azure Active Directory and Context-Aware Access, which enforce granular permissions.++### How to Implement Access Control and Authentication++Start by mapping out who needs what data and why. From there, you can build a robust system that protects sensitive information without hindering productivity.++* **Implement a Zero-Trust Model:** Assume no user or device is inherently trustworthy, even if it's inside your network. Verify every access request. This means requiring strong authentication like Multi-Factor Authentication (MFA) for all users, especially those accessing sensitive systems.+* **Use Role-Based Access Control (RBAC):** Instead of assigning permissions one by one, create roles (e.g., "Developer," "Support Agent") with pre-defined access levels. This simplifies management and reduces human error. When an employee changes roles, you just change their assigned role, and their permissions update automatically.+* **Conduct Quarterly Access Reviews:** Don't set it and forget it. Regularly review who has access to what. This helps you catch and revoke outdated permissions for former employees or those who have changed roles, closing a common security gap in data privacy best practices.++## 4. Privacy by Design++Privacy by Design is a proactive approach that embeds privacy into the very fabric of your systems and business practices. Instead of bolting on privacy features as an afterthought to fix a problem, you build them in from the initial design phase. It’s about making privacy the default setting, ensuring that user data is protected automatically without them having to take any action. This is one of the most fundamental data privacy best practices for building long-term user trust.++This methodology, championed by Dr. Ann Cavoukian and foundational to GDPR, shifts the responsibility of data protection from the user to the company. Apple's on-device processing and robust privacy controls in iOS are a prime example. Similarly, the Brave browser's architecture is built from the ground up to block trackers and ads by default, making privacy an inherent part of the user experience.++### How to Implement Privacy by Design++Start by involving privacy experts in your initial product meetings, not just in your final compliance checks. The goal is to make privacy a core requirement, just like functionality or user experience.++* **Conduct Privacy Impact Assessments (PIAs):** Before you even write a line of code, conduct a PIA to identify and mitigate potential privacy risks associated with a new project. This helps you anticipate problems before they happen.+* **Default to Privacy-Enhancing Settings:** Make the most private settings the default for any new feature. Users should have to opt-in to share more data, not opt-out to protect their existing privacy.+* **Build User Control Panels:** Create a clear, accessible privacy dashboard where users can easily understand and manage their data settings. Give them granular control over what they share and how it’s used.++## 5. Regular Privacy Audits and Assessments++Regular privacy audits are like a scheduled health check-up for your company's data practices. They are systematic reviews of your data handling processes, policies, and security measures to ensure you’re not just compliant on paper, but also in practice. This isn't a one-and-done task; it's a continuous cycle of evaluation and improvement that keeps your organization accountable and resilient.++Think of the rigorous HIPAA risk assessments healthcare organizations must undergo or the GDPR compliance reviews tech companies now treat as standard procedure. These audits aren't just for avoiding fines. They build trust by demonstrating a proactive commitment to protecting user information, turning a potential liability into a genuine brand asset. A consistent audit schedule is a core component of robust data privacy best practices.++### How to Implement Regular Privacy Audits++The key is to make audits a predictable, routine part of your operations, not a frantic reaction to a problem.++* **Establish a Regular Cadence:** Don't wait for a crisis. Schedule comprehensive privacy audits on a quarterly or bi-annual basis to catch issues before they escalate. Treat it with the same importance as a financial audit.+* **Engage Third-Party Auditors:** While internal reviews are good, an external auditor brings an unbiased, expert perspective. They can identify blind spots your team might miss and provide an objective assessment of your compliance posture.+* **Create Actionable Remediation Plans:** An audit is only useful if you act on its findings. For every identified vulnerability, create a clear remediation plan with assigned owners, specific deadlines, and a process for verifying that the fix has been implemented successfully.++## 6. Data Breach Response Plan++A data breach response plan is your organization's fire drill for a digital crisis. It’s a comprehensive, pre-established protocol outlining the exact steps to take the moment a breach is detected. Having a plan isn't just a good idea; it's a critical component of data privacy best practices that ensures a swift, coordinated response to minimize damage, meet legal notification requirements under laws like GDPR, and begin the recovery process.++The goal is to move from chaos to control. A well-rehearsed plan prevents panic and ensures every action is deliberate and effective. Companies like Capital One demonstrated this by quickly reporting their breach to regulators and initiating customer outreach, which helped manage the fallout. Without a plan, teams scramble, evidence is lost, and customer trust evaporates.++The infographic below illustrates the immediate, core stages of a typical data breach response flow.++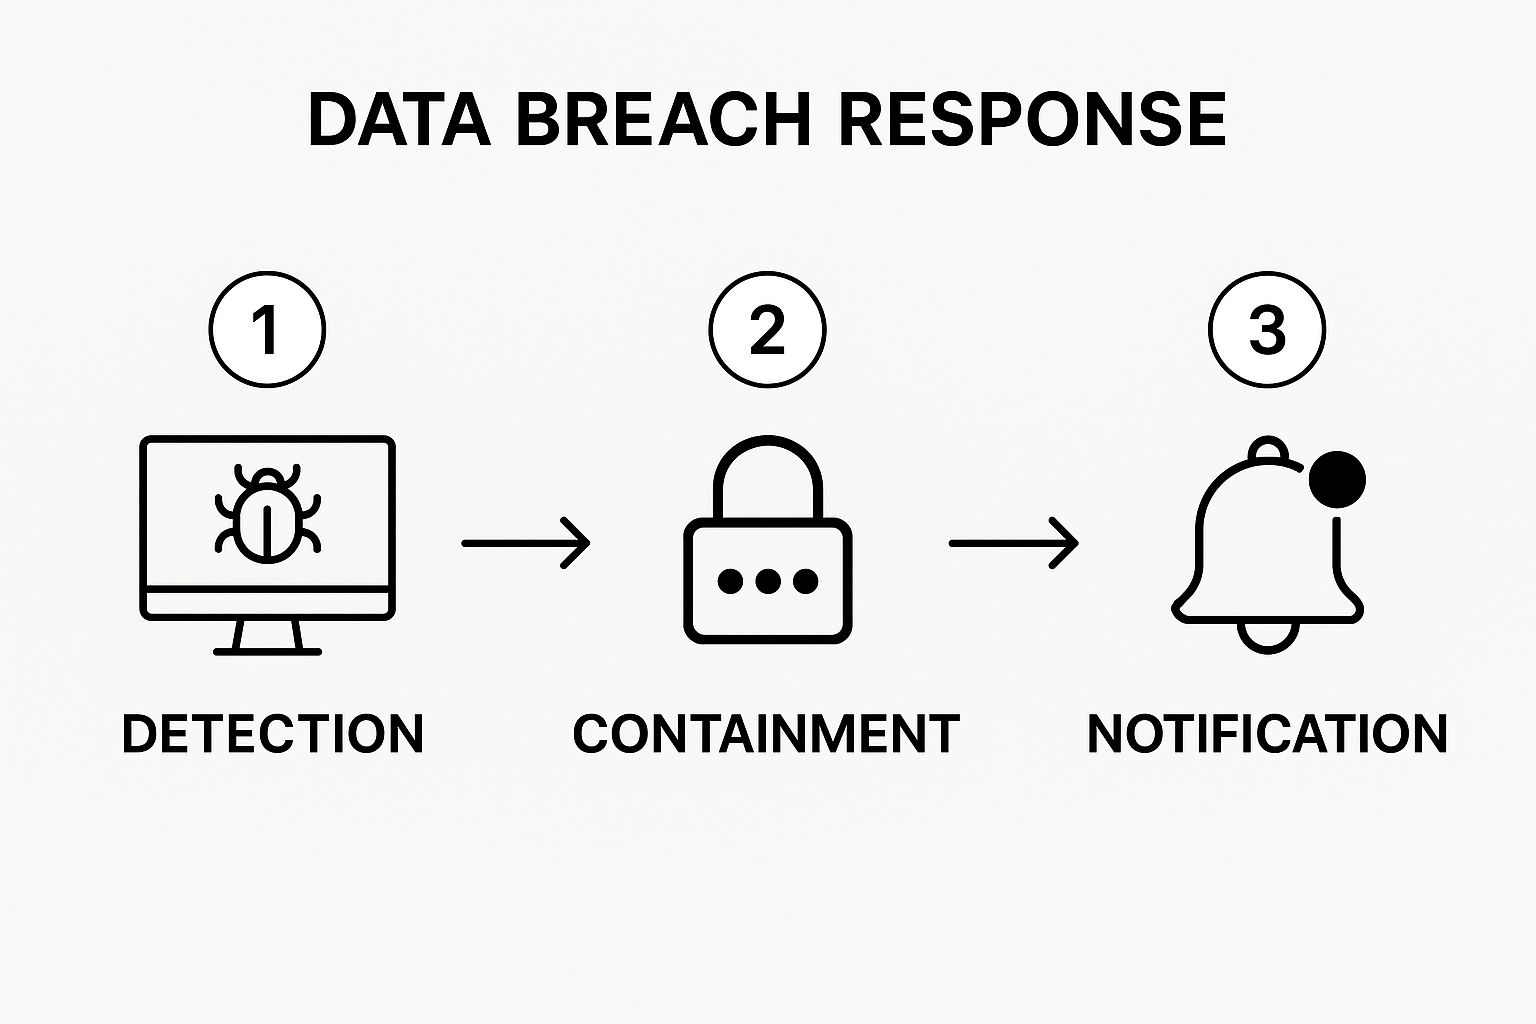++This process flow emphasizes that immediate containment is the critical bridge between detecting a threat and properly notifying affected parties.++### How to Implement a Data Breach Response Plan++It’s not enough to just write a plan; you have to make it an active part of your security posture. Here’s how to get started:++* **Conduct Tabletop Exercises:** Regularly simulate a data breach scenario with your response team. These "fire drills" test the plan's effectiveness, reveal weaknesses, and ensure everyone knows their role under pressure without impacting live systems.+* **Prepare Communication Templates:** Don't write your customer notifications or regulatory statements in the middle of a crisis. Pre-draft and get legal approval for communication templates for different scenarios. This ensures your messaging is clear, empathetic, and compliant.+* **Establish Key Relationships:** Build relationships with external experts **before** you need them. This includes cybersecurity forensic investigators, legal counsel specializing in privacy law, and public relations firms. Have their contact information and contracts ready to go.++<iframe width="560" height="315" src="https://www.youtube.com/embed/XP_Vz68_c7M" frameborder="0" allow="accelerometer; autoplay; clipboard-write; encrypted-media; gyroscope; picture-in-picture" allowfullscreen></iframe>++## 7. User Consent Management++User consent management is the process of asking for, recording, and managing a user’s permission before you collect or process their personal data. It’s about being upfront and giving users genuine control, turning the old model of "collect first, ask questions later" completely on its head. This isn't just a pop-up banner; it's a foundational element of earning user trust and a non-negotiable requirement under laws like GDPR.++Effective consent management respects user autonomy. Think of Apple's App Tracking Transparency (ATT) framework, which requires apps to get explicit permission before tracking users across other companies' apps and websites. Platforms like OneTrust and Cookiebot have built entire businesses around helping companies manage this complex process, providing tools to create clear, compliant consent experiences.++### How to Implement User Consent Management++True consent is freely given, specific, informed, and unambiguous. The key is to make giving and withdrawing consent equally straightforward.++* **Use Clear, Jargon-Free Language:** Don't hide behind legalistic terms. Instead of "We may use third-party processors to optimize user-centric paradigms," say "We use tools like Google Analytics to understand how you use our site. Can we turn this on?"+* **Provide Granular Options:** Allow users to opt into specific data uses, like "Essential Cookies" versus "Marketing Cookies," rather than forcing an all-or-nothing choice. This respects their preferences and is a core component of modern data privacy best practices.+* **Make Withdrawal Effortless:** Users should be able to change their mind at any time. Ensure your privacy settings dashboard is easy to find and use, making the process of withdrawing consent as simple as the initial opt-in.++## 8. Third-Party Vendor Management++Your company's data privacy is only as strong as its weakest link, and that weak link is often a third-party vendor. Third-party vendor management is the process of vetting, monitoring, and holding your partners accountable for protecting the data you entrust to them. You can have fortress-like internal security, but it means nothing if your marketing analytics tool gets breached and leaks all your customer data.++This practice is non-negotiable in a world of interconnected SaaS tools. A data breach at one of your vendors is a data breach for you, both legally and reputationally. Major cloud providers like Amazon Web Services (AWS) and Microsoft Azure address this with comprehensive data processing agreements and security certifications, setting a clear standard for how vendors should handle customer data responsibly.++### How to Implement Third-Party Vendor Management++Effective management starts before you sign any contract and continues long after. It's about asking: **"Can I trust this partner with my users' data?"**++* **Maintain a Vendor Inventory:** You can't protect what you don't know you have. Keep a detailed, up-to-date list of all third-party vendors, what data they access, and for what purpose. This is a foundational step in any serious data privacy best practices program.+* **Insist on Contractual Protections:** Your contracts must include specific data privacy clauses. Require vendors to notify you immediately in the event of a breach, outline their security measures, and comply with regulations like GDPR. For healthcare, this means having a signed HIPAA Business Associate Agreement.+* **Conduct Regular Privacy Assessments:** Don't just take their word for it. Periodically review your vendors' security postures. Ask for their latest security audit reports (like SOC 2) or privacy certifications to ensure they are still meeting the standards you require.++## 9. Employee Training and Awareness++Your security tools and privacy policies are only as strong as your weakest link, which is often an uninformed employee. Employee training and awareness programs are designed to transform your team from a potential liability into your first line of defense. This involves educating every employee on their responsibilities, how to handle personal data, and how to spot potential privacy risks. It’s a foundational element of a robust data privacy strategy.++A well-intentioned employee clicking on a phishing link can compromise more data than a faulty firewall. Organizations like the IAPP and SANS Institute have built entire frameworks around this principle. Similarly, companies in regulated sectors like healthcare and finance make HIPAA and data protection training a mandatory, recurring event. These programs are not just about compliance; they build a culture of security where protecting data is everyone’s job.++### How to Implement Employee Training and Awareness++Building an effective program is about making training engaging, relevant, and continuous. A one-off seminar during onboarding is simply not enough.++* **Make Training Interactive and Scenario-Based:** Ditch the dry, text-heavy slideshows. Use real-world scenarios, quizzes, and role-playing exercises. Platforms like KnowBe4 use phishing simulations to test and train employees in a controlled environment, making the lessons stick.+* **Provide Regular Updates on Regulations:** The privacy landscape is constantly changing. Schedule brief, regular updates on new laws like GDPR or CCPA to ensure your team’s knowledge is always current. This keeps data privacy best practices top of mind.+* **Recognize and Reward Good Practices:** Create a positive feedback loop. Publicly acknowledge employees who report potential phishing attempts or identify privacy risks. This encourages proactive behavior and reinforces the importance of the training.++## Data Privacy Best Practices Comparison++| Item | Implementation Complexity 🔄 | Resource Requirements ⚡ | Expected Outcomes 📊 | Ideal Use Cases 💡 | Key Advantages ⭐ |+|---------------------------------|-----------------------------------------|-----------------------------------------|--------------------------------------------------|------------------------------------------|----------------------------------------------|+| Data Minimization | Medium - requires careful planning and ongoing audits | Moderate - initial setup resource-intensive | Reduced breach risk, improved data quality, regulatory compliance | Organizations prioritizing minimal data collection and privacy by design | Lowers risk exposure, compliance costs, builds trust |+| Encryption at Rest and in Transit| High - complex key management and maintenance | High - robust infrastructure needed | Strong data protection during storage and transmission | Systems handling sensitive data in transit and at rest | Protects data integrity, meets compliance standards |+| Access Control and Authentication| High - complex policies, MFA, and monitoring | High - ongoing administration and infrastructure | Prevents unauthorized access, audit trails, reduces insider threats | Enterprises with diverse user roles and sensitive data | Enhances security, supports compliance, reduces insider risk |+| Privacy by Design | High - requires specialized privacy expertise and upfront investment | High - involves privacy experts during design | Comprehensive privacy built into products, regulatory compliance from start | Development of new products/services prioritizing privacy | Reduces retrofitting costs, boosts user trust and compliance |+| Regular Privacy Audits and Assessments | Medium to High - requires expertise, time, and coordination | High - resource-intensive and periodic | Identifies risks, ensures compliance, improves governance | Organizations subject to strict regulations requiring accountability | Proactive risk detection, compliance demonstration |+| Data Breach Response Plan | Medium - requires defined protocols and regular updates | Moderate to High - testing and maintenance needed | Minimized breach impact, fast recovery, compliance with notification laws | All organizations needing a structured breach response | Limits damage, preserves trust, ensures legal compliance |+| User Consent Management | Medium - requires clear interfaces and ongoing updates | Moderate - system development and management | Legal data processing basis, enhanced user trust | Consumer-facing platforms requiring explicit consent | Builds transparency and regulatory compliance |+| Third-Party Vendor Management | Medium to High - continuous vendor assessment and contract management | Moderate to High - ongoing monitoring | Reduced third-party risks, ensures privacy across ecosystem | Companies relying on multiple external vendors | Extends privacy protection and compliance chain |+| Employee Training and Awareness | Medium - recurring training and awareness programs | Moderate - continuous investment in content and delivery | Reduced human error, culture of privacy, better incident reporting | All organizations aiming to minimize insider threats and ensure compliance | Enhances privacy culture, reduces risks due to human error |++## Putting It All Together: Your Next Steps in Data Privacy++We've covered a lot of ground, from the technical nuts and bolts of encryption to the big-picture strategy of Privacy by Design. It’s easy to look at a list of nine comprehensive data privacy best practices and feel a little overwhelmed. But here's the secret: you don't have to boil the ocean overnight. True mastery of data privacy isn't about a single, massive overhaul; it's about building a sustainable culture of respect for user information through consistent, incremental improvements.++Think of it like building a fortress. You wouldn't try to construct all the walls, moats, and watchtowers in a single day. You'd start with a solid foundation (your privacy policy and data minimization), then build the first wall (strong access controls), and then add another layer of defense (encryption). Each practice we've discussed is another stone in your fortress, making your organization more resilient, trustworthy, and secure.++### From Theory to Action: Your Privacy Roadmap++The most important takeaway is that **action creates momentum**. Reading about these principles is great, but implementing them is what truly protects your users and your business. The journey from good intentions to a robust privacy framework starts with a single step.++Here’s a simple, actionable plan to get you started right now:++1. **Conduct a Mini-Audit:** Pick just one of your core processes, like user sign-up or a marketing campaign. Ask yourself the tough questions based on what we've covered. Are you collecting only the data you absolutely need? Is consent clear and easy to withdraw? This small-scale review will reveal immediate opportunities for improvement without feeling like a monumental task.+2. **Tackle One High-Impact Area:** Don't try to fix everything at once. Maybe your biggest vulnerability is a lack of a formal data breach response plan. Or perhaps your team could really benefit from dedicated employee awareness training. Choose the one area that will provide the biggest security and trust boost, and focus your energy there for the next month.+3. **Empower Your Team:** Share this article. Start a conversation in your team's chat channel about one of these practices. Fostering a shared understanding and responsibility is crucial. When your entire team views privacy as a core feature, not an obstacle, you've already won half the battle.++Ultimately, embracing these data privacy best practices is more than a compliance checkbox; it's a powerful business differentiator. In a world where users are increasingly skeptical of how their data is handled, being a transparent and trustworthy steward of their information builds unshakable brand loyalty. You're not just avoiding fines; you're building a reputation that attracts and retains customers who value their privacy. This proactive, user-centric approach is the cornerstone of a modern, resilient, and respected business.++***++Ready to put these principles into practice without sacrificing powerful analytics? **Rybbit Analytics** is built from the ground up to be privacy-first, giving you the insights you need while respecting your users' data. See how our cookieless, compliance-focused platform makes implementing data privacy best practices simple by visiting [Rybbit Analytics](https://www.rybbit.io) today.\ No newline at end of filediff --git a/docs-v2/next.config.mjs b/docs-v2/next.config.mjsindex 46f3196e2..896821ba0 100644--- a/docs-v2/next.config.mjs+++ b/docs-v2/next.config.mjs@@ -1,4 +1,4 @@-import { createMDX } from 'fumadocs-mdx/next';+import { createMDX } from "fumadocs-mdx/next";const withMDX = createMDX();@@ -8,16 +8,20 @@ const config = {images: {remotePatterns: [{- protocol: 'https',- hostname: 'pbs.twimg.com',+ protocol: "https",+ hostname: "pbs.twimg.com",},{- protocol: 'https',- hostname: 'abs.twimg.com',+ protocol: "https",+ hostname: "abs.twimg.com",},{- protocol: 'https',- hostname: 'ui-avatars.com',+ protocol: "https",+ hostname: "ui-avatars.com",+ },+ {+ protocol: "https",+ hostname: "cdn.outrank.so",},],},diff --git a/docs-v2/src/app/blog/[...slug]/page.tsx b/docs-v2/src/app/blog/[...slug]/page.tsxindex 669e1a349..3efb23588 100644--- a/docs-v2/src/app/blog/[...slug]/page.tsx+++ b/docs-v2/src/app/blog/[...slug]/page.tsx@@ -6,6 +6,7 @@ import { ChevronLeft } from 'lucide-react';import type { Metadata } from 'next';import defaultMdxComponents from 'fumadocs-ui/mdx';import { Pre } from 'fumadocs-ui/components/codeblock';+import Script from 'next/script';export function generateStaticParams() {return blogSource.getPages().map((page) => ({@@ -18,9 +19,43 @@ export async function generateMetadata(props: { params: Promise<{ slug: string[]const page = blogSource.getPage(params.slug);if (!page) return {};+ const url = `https://docs.rybbit.io/blog/${params.slug.join('/')}`;+ const publishedTime = page.data.date ? new Date(page.data.date).toISOString() : undefined;+ const ogImage = page.data.image || '/opengraph-image.png';+return {title: page.data.title,description: page.data.description,+ alternates: {+ canonical: url,+ },+ openGraph: {+ title: page.data.title,+ description: page.data.description,+ type: 'article',+ publishedTime,+ authors: page.data.author ? [page.data.author] : undefined,+ url,+ images: [+ {+ url: ogImage,+ width: 1200,+ height: 630,+ alt: page.data.title,+ },+ ],+ siteName: 'Rybbit',+ locale: 'en_US',+ },+ twitter: {+ card: 'summary_large_image',+ title: page.data.title,+ description: page.data.description,+ images: [ogImage],+ creator: '@rybbitio',+ },+ keywords: page.data.tags ? [...page.data.tags, 'web analytics', 'privacy analytics', 'Rybbit'] : ['web analytics', 'privacy analytics', 'Rybbit'],+ authors: page.data.author ? [{ name: page.data.author }] : undefined,};}@@ -34,9 +69,43 @@ export default async function BlogPostPage(props: { params: Promise<{ slug: striconst MDXContent = page.data.body;const date = page.data.date ? new Date(page.data.date) : null;++ // Structured data for SEO+ const structuredData = {+ '@context': 'https://schema.org',+ '@type': 'BlogPosting',+ headline: page.data.title,+ description: page.data.description,+ image: page.data.image || 'https://docs.rybbit.io/opengraph-image.png',+ datePublished: date?.toISOString(),+ dateModified: date?.toISOString(),+ author: {+ '@type': 'Person',+ name: page.data.author || 'Rybbit Team',+ },+ publisher: {+ '@type': 'Organization',+ name: 'Rybbit',+ logo: {+ '@type': 'ImageObject',+ url: 'https://docs.rybbit.io/rybbit.png',+ },+ },+ mainEntityOfPage: {+ '@type': 'WebPage',+ '@id': `https://docs.rybbit.io/blog/${params.slug.join('/')}`,+ },+ keywords: page.data.tags?.join(', '),+ };return (- <article className="max-w-4xl mx-auto px-4 py-16">+ <>+ <Script+ id="structured-data"+ type="application/ld+json"+ dangerouslySetInnerHTML={{ __html: JSON.stringify(structuredData) }}+ />+ <article className="max-w-4xl mx-auto px-4 py-16"><Linkhref="/blog"className="inline-flex items-center text-neutral-400 hover:text-white transition-colors mb-8"@@ -122,5 +191,6 @@ export default async function BlogPostPage(props: { params: Promise<{ slug: stri}} /></div></article>+ </>);}\ No newline at end of filediff --git a/docs-v2/src/app/layout.tsx b/docs-v2/src/app/layout.tsxindex ab923b8cb..ec2358938 100644--- a/docs-v2/src/app/layout.tsx+++ b/docs-v2/src/app/layout.tsx@@ -2,12 +2,65 @@ import "@/app/global.css";import { RootProvider } from "fumadocs-ui/provider";import { Inter } from "next/font/google";import type { ReactNode } from "react";+import type { Metadata } from "next";const inter = Inter({subsets: ["latin"],variable: "--font-inter",});+export const metadata: Metadata = {+ title: {+ default: "Rybbit - Privacy-First Web Analytics Platform",+ template: "%s | Rybbit"+ },+ description: "Open-source, privacy-focused web analytics platform. Track your website performance without compromising user privacy. Self-hostable alternative to Google Analytics.",+ keywords: ["web analytics", "privacy analytics", "open source analytics", "Google Analytics alternative", "website tracking", "self-hosted analytics"],+ authors: [{ name: "Rybbit Team" }],+ creator: "Rybbit",+ publisher: "Rybbit",+ metadataBase: new URL("https://rybbit.io"),+ openGraph: {+ type: "website",+ locale: "en_US",+ url: "https://rybbit.io",+ siteName: "Rybbit",+ title: "Rybbit - Privacy-First Web Analytics Platform",+ description: "Open-source, privacy-focused web analytics platform. Track your website performance without compromising user privacy.",+ images: [+ {+ url: "/opengraph-image.png",+ width: 1200,+ height: 630,+ alt: "Rybbit Analytics Dashboard"+ }+ ]+ },+ twitter: {+ card: "summary_large_image",+ title: "Rybbit - Privacy-First Web Analytics Platform",+ description: "Open-source, privacy-focused web analytics platform. Track your website performance without compromising user privacy.",+ images: ["/opengraph-image.png"],+ creator: "@rybbitio"+ },+ robots: {+ index: true,+ follow: true,+ googleBot: {+ index: true,+ follow: true,+ "max-video-preview": -1,+ "max-image-preview": "large",+ "max-snippet": -1+ }+ },+ verification: {+ google: "",+ yandex: "",+ yahoo: ""+ }+};+export default function Layout({ children }: { children: ReactNode }) {return (<html lang="en" suppressHydrationWarning className="dark">diff --git a/docs-v2/src/app/robots.ts b/docs-v2/src/app/robots.tsnew file mode 100644index 000000000..5bb27064a--- /dev/null+++ b/docs-v2/src/app/robots.ts@@ -0,0 +1,32 @@+import { MetadataRoute } from 'next';++export default function robots(): MetadataRoute.Robots {+ const baseUrl = 'https://docs.rybbit.io';++ return {+ rules: [+ {+ userAgent: '*',+ allow: '/',+ disallow: [+ '/api/',+ '/_next/',+ '/static/',+ '/*.json$',+ '/*?*', // URLs with query parameters+ '/404',+ ],+ },+ {+ userAgent: 'Googlebot',+ allow: '/',+ },+ {+ userAgent: 'Bingbot',+ allow: '/',+ },+ ],+ sitemap: `${baseUrl}/sitemap.xml`,+ host: baseUrl,+ };+}\ No newline at end of filediff --git a/docs-v2/src/app/sitemap.ts b/docs-v2/src/app/sitemap.tsnew file mode 100644index 000000000..66846f04b--- /dev/null+++ b/docs-v2/src/app/sitemap.ts@@ -0,0 +1,53 @@+import { MetadataRoute } from 'next';+import { source } from '@/lib/source';+import { blogSource } from '@/lib/blog-source';++export default async function sitemap(): Promise<MetadataRoute.Sitemap> {+ const baseUrl = 'https://docs.rybbit.io';++ // Get all documentation pages+ const docPages = source.getPages().map((page) => ({+ url: `${baseUrl}/docs/${page.slugs.join('/')}`,+ lastModified: page.data.lastModified || new Date(),+ changeFrequency: 'weekly' as const,+ priority: 0.8,+ }));++ // Get all blog posts+ const blogPosts = blogSource.getPages().map((post) => ({+ url: `${baseUrl}/blog/${post.slugs.join('/')}`,+ lastModified: post.data.date || new Date(),+ changeFrequency: 'monthly' as const,+ priority: 0.7,+ }));++ // Static pages+ const staticPages = [+ {+ url: baseUrl,+ lastModified: new Date(),+ changeFrequency: 'daily' as const,+ priority: 1.0,+ },+ {+ url: `${baseUrl}/docs`,+ lastModified: new Date(),+ changeFrequency: 'weekly' as const,+ priority: 0.9,+ },+ {+ url: `${baseUrl}/blog`,+ lastModified: new Date(),+ changeFrequency: 'weekly' as const,+ priority: 0.8,+ },+ {+ url: `${baseUrl}/pricing`,+ lastModified: new Date(),+ changeFrequency: 'monthly' as const,+ priority: 0.6,+ },+ ];++ return [...staticPages, ...docPages, ...blogPosts];+}\ No newline at end of file