
Find, verify, and analyze leaked credentials
Go credentialsdevsecopsdynamic-analysisprecommitscanningsecretsecret-managementsecretssecuritysecurity-toolstrufflehogverification
Update README.md with Windows-specific Docker installation instructions (#2674)
Jacinto27ccd191011204
diff --git a/README.md b/README.mdindex 5d0f2f0ba..0379bd8bf 100644--- a/README.md+++ b/README.md@@ -46,30 +46,68 @@ docker run --rm -it -v "$PWD:/pwd" trufflesecurity/trufflehog:latest github --orSeveral options available for you:+### MacOS users+```bash-# MacOS usersbrew install trufflehog+```++### Docker:++<sub><i>*Ensure Docker engine is running before executing the following commands:*</i></sub>++#### Unix-# Docker+```bashdocker run --rm -it -v "$PWD:/pwd" trufflesecurity/trufflehog:latest github --repo https://github.com/trufflesecurity/test_keys+```++#### Windows Command Prompt-# Docker for M1 and M2 Mac+```bash+docker run --rm -it -v "%cd:/=\%:/pwd" trufflesecurity/trufflehog:latest github --repo https://github.com/trufflesecurity/test_keys+```++#### Windows PowerShell++```bash+docker run --rm -it -v "${PWD}:/pwd" trufflesecurity/trufflehog github --repo https://github.com/trufflesecurity/test_keys+```++#### M1 and M2 Mac++```bashdocker run --platform linux/arm64 --rm -it -v "$PWD:/pwd" trufflesecurity/trufflehog:latest github --repo https://github.com/trufflesecurity/test_keys+```++### Binary releases-# Binary releases+```bashDownload and unpack from https://github.com/trufflesecurity/trufflehog/releases+```++### Compile from source-# Compile from source+```bashgit clone https://github.com/trufflesecurity/trufflehog.gitcd trufflehog; go install+```-# Using installation script+### Using installation script++```bashcurl -sSfL https://raw.githubusercontent.com/trufflesecurity/trufflehog/main/scripts/install.sh | sh -s -- -b /usr/local/bin+```++### Using installation script, verify checksum signature (requires cosign to be installed)-# Using installation script, verify checksum signature (requires cosign to be installed)+```bashcurl -sSfL https://raw.githubusercontent.com/trufflesecurity/trufflehog/main/scripts/install.sh | sh -s -- -v -b /usr/local/bin+```++### Using installation script to install a specific version-# Using installation script to install a specific version+```bashcurl -sSfL https://raw.githubusercontent.com/trufflesecurity/trufflehog/main/scripts/install.sh | sh -s -- -b /usr/local/bin <ReleaseTag like v3.56.0>```@@ -159,7 +197,7 @@ Expected output:...```-## 4: Scan a GitHub Repo + its Issues and Pull Requests.+## 4: Scan a GitHub Repo + its Issues and Pull Requests```bashtrufflehog github --repo=https://github.com/trufflesecurity/test_keys --issue-comments --pr-comments@@ -189,13 +227,13 @@ docker run --rm -v "$HOME/.ssh:/root/.ssh:ro" trufflesecurity/trufflehog:latesttrufflehog filesystem path/to/file1.txt path/to/file2.txt path/to/dir```-## 9: Scan GCS buckets for verified secrets.+## 9: Scan GCS buckets for verified secrets```bashtrufflehog gcs --project-id=<project-ID> --cloud-environment --only-verified```-## 10: Scan a Docker image for verified secrets.+## 10: Scan a Docker image for verified secretsUse the `--image` flag multiple times to scan multiple images.@@ -319,7 +357,7 @@ Args:For example, to scan a `git` repository, start with```-$ trufflehog git https://github.com/trufflesecurity/trufflehog.git+trufflehog git https://github.com/trufflesecurity/trufflehog.git```## S3@@ -379,7 +417,6 @@ jobs:In the example config above, we're scanning for live secrets in all PRs and Pushes to `main`. Only code changes in the referenced commits are scanned. If you'd like to scan an entire branch, please see the "Advanced Usage" section below.-### Shallow CloningIf you're incorporating TruffleHog into a standalone workflow and aren't running any other CI/CD tooling alongside TruffleHog, then we recommend using [Shallow Cloning](https://git-scm.com/docs/git-clone#Documentation/git-clone.txt---depthltdepthgt) to speed up your workflow. Here's an example for how to do it:@@ -409,6 +446,7 @@ If you're incorporating TruffleHog into a standalone workflow and aren't runningDepending on the event type (push or PR), we calculate the number of commits present. Then we add 2, so that we can reference a base commit before our code changes. We pass that integer value to the `fetch-depth` flag in the checkout action in addition to the relevant branch. Now our checkout process should be much shorter.### Canary detection+TruffleHog statically detects [https://canarytokens.org/](https://canarytokens.org/) and lets you know when they're present without setting them off. You can learn more here: [https://trufflesecurity.com/canaries](https://trufflesecurity.com/canaries)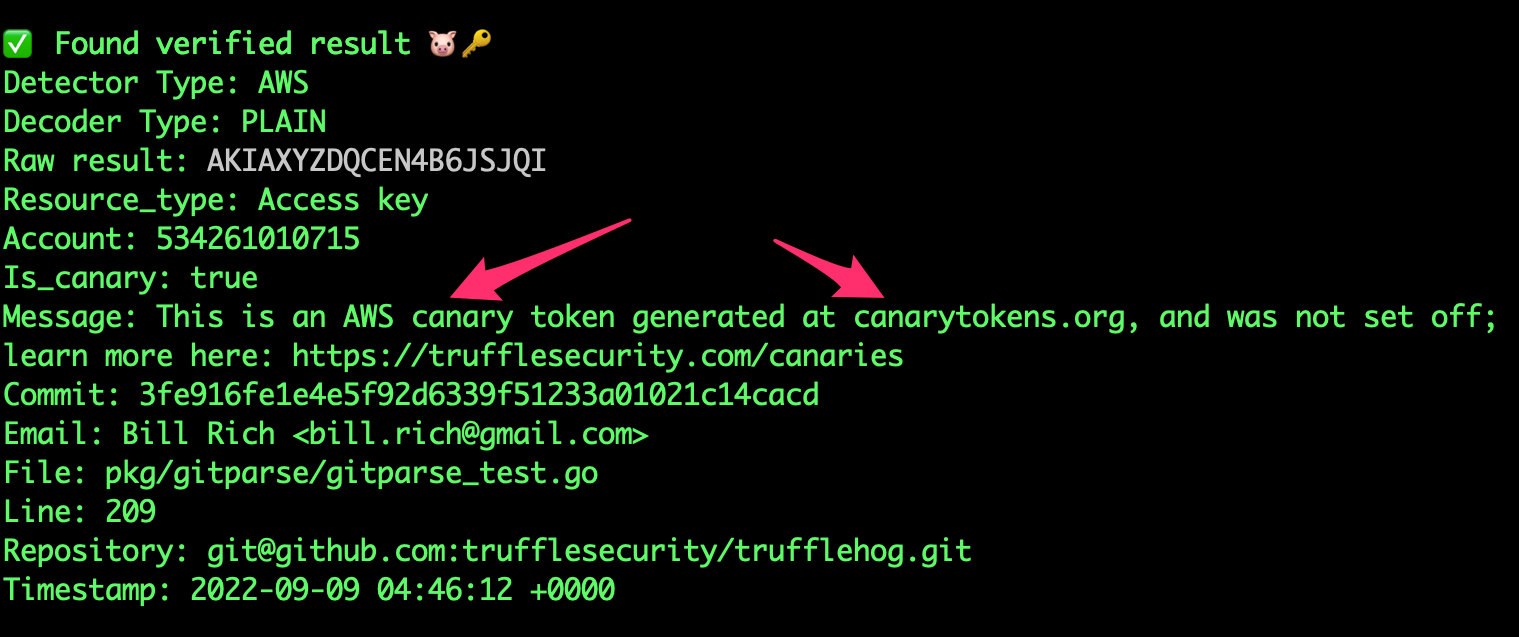@@ -432,6 +470,7 @@ TruffleHog statically detects [https://canarytokens.org/](https://canarytokens.oIf you'd like to specify specific `base` and `head` refs, you can use the `base` argument (`--since-commit` flag in TruffleHog CLI) and the `head` argument (`--branch` flag in the TruffleHog CLI). We only recommend using these arguments for very specific use cases, where the default behavior does not work.#### Advanced Usage: Scan entire branch+```- name: scan-pushuses: trufflesecurity/trufflehog@main@@ -524,7 +563,6 @@ detectors:- "Authorization: super secret authorization header"```-```$ trufflehog filesystem /tmp --config config.yaml --only-verified🐷🔑🐷 TruffleHog. Unearth your secrets. 🐷🔑🐷@@ -535,6 +573,7 @@ Decoder Type: PLAINRaw result: HOGAAIUNNWHAHJJWUQYRFile: /tmp/hog-facts.txt```+Data structure sent to the custom verification server:```@@ -625,6 +664,6 @@ Since v3.0, TruffleHog is released under a AGPL 3 license, included in [`LICENSE# :money_with_wings: Enterprise product-Are you interested in continuously monitoring your Git, Jira, Slack, Confluence, etc.. for credentials? We have an enterprise product that can help. Reach out here to learn more https://trufflesecurity.com/contact/+Are you interested in continuously monitoring your Git, Jira, Slack, Confluence, etc.. for credentials? We have an enterprise product that can help. Reach out here to learn more <https://trufflesecurity.com/contact/>We take the revenue from the enterprise product to fund more awesome open source projects that the whole community can benefit from.